Skip to content
IonWarpTry for free

Snyk alternative

The Snyk alternative for teams whose risk is in their own code.

Snyk prices each developer; IonWarp prices the team. It reviews the code your team and its agents write — a missing tenant check, an unquoted input, a key sent to a model — on the pull requests that need it, with Code Review on each one. Keep GitHub's free Dependabot for your packages.

  • Starter is free for 3 people
  • One team price: Pro is $49/mo for 5 seats
  • Read-only GitHub App
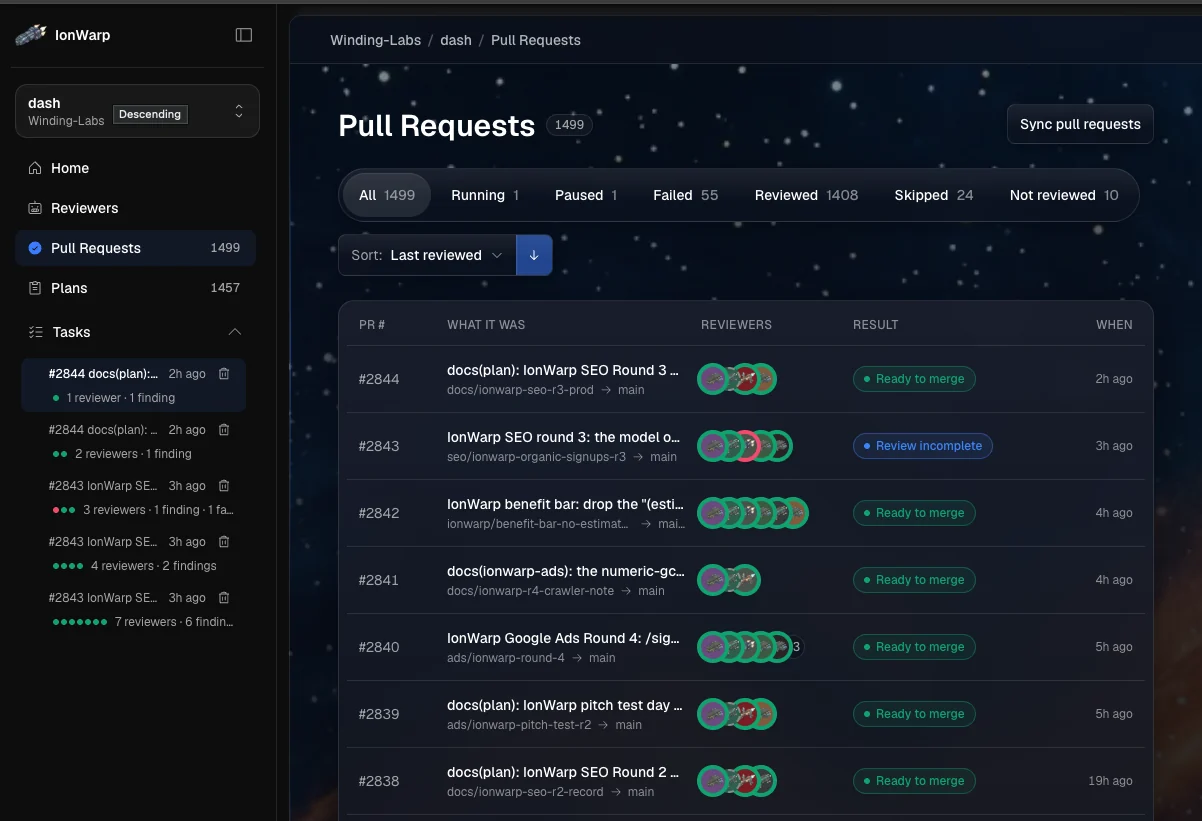
IonWarp's Pull Requests page for its own repository: 1,499 pull requests, each row with the reviewers that ran on it and its result.
52security P0/P1 findings fixedIonWarp's own pull requests, Aug 27 – Nov 2
$0.04model cost of one reviewAI Architecture · DeepSeek V4.1 Flash · 58 s

What it caught in IonWarp's own code

Catches the query that reads every customer's rows

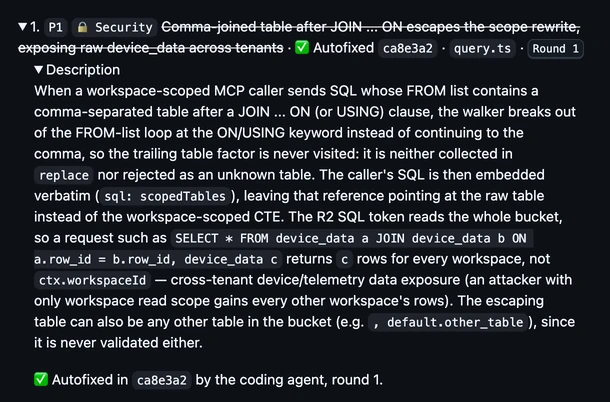
A comma-joined table after a JOIN slipped past a workspace scope rewrite, so a key that could read one workspace could read every workspace's device data. The finding named the query, who could abuse it and what they would get; the coding agent fixed it in round 1.

A P1 security finding on one of IonWarp's own pull requests: a comma-joined table after JOIN … ON escapes the workspace scope rewrite, so one workspace's read key reads every workspace's device data — autofixed in round 1.

Sees a secret leave through a prompt

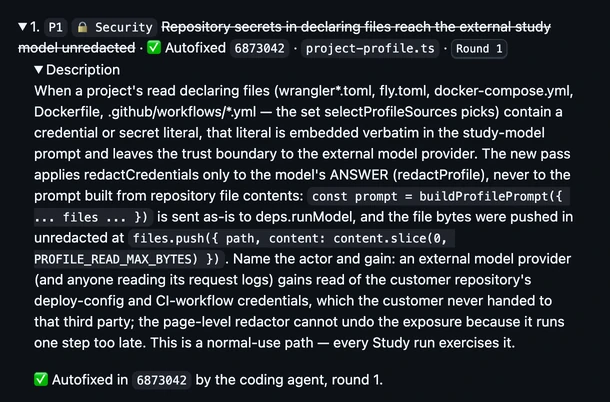
A new pass read a repository's deploy config files into a prompt for an outside model and redacted only the answer, so any credential in those files went to the model provider. A pattern scanner has no rule for that; the fix moved redaction before the prompt.

A P1 security finding on one of IonWarp's own pull requests: credentials in a repository's deploy config files are copied unredacted into a prompt for an outside model — autofixed in round 1.

Finds the input that reaches a shell

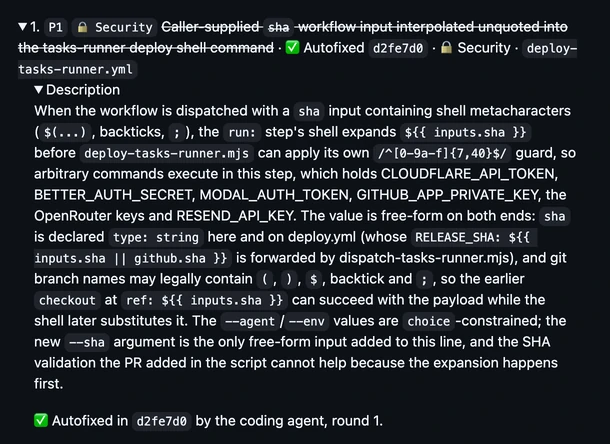
A deploy workflow put a caller's `sha` input into a shell command unquoted, in a step that holds the deploy keys. The finding showed why the script's own check came too late: the shell expands the input first.

A P1 security finding on one of IonWarp's own pull requests: a caller-supplied workflow input is put unquoted into a shell command in a step that holds the deploy keys — autofixed in round 1.

Specialists join when the diff needs them

A planner reads each pull request and adds the reviewers it needs beside Code Review: security, architecture, performance, docs, SEO, analytics or UX. Each runs on the plans shown.

  • 16 reviewers in the catalog
  • One GitHub comment for all of them
  • Each reviewer's findings are labeled with its name
  • Code ReviewEvery plan
  • Security ReviewEvery plan
  • AI ArchitecturePro
  • API PerformanceMax
  • Docs ReviewPro
  • SEO ReviewMax
  • Analytics ReviewMax
  • UX ReviewMax

Your agent closes it; IonWarp checks the fix

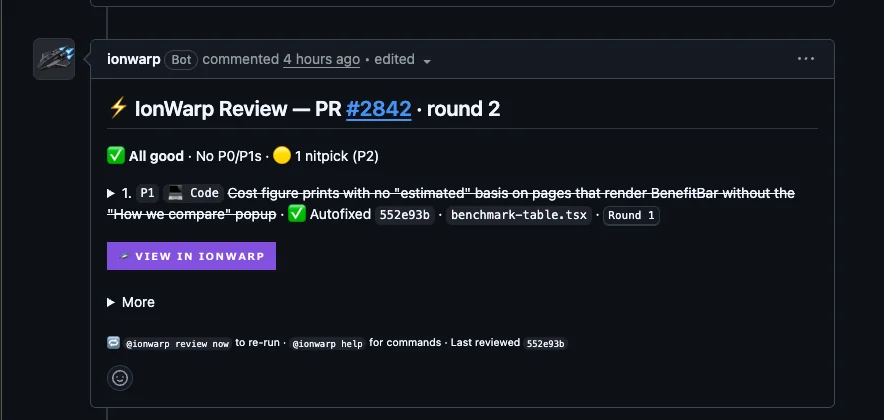
Every finding carries a fix prompt for Claude Code, Cursor or Codex. The GitHub App is read-only, so it never pushes: your agent pushes the fix, and IonWarp re-reviews and strikes the finding through as Autofixed, or keeps it open.

An IonWarp review comment in round 2: no P0 or P1 left, and a round-1 P1 struck through and marked Autofixed with its commit.

Each reviewer's model, cost and time

Every review comment ends with a table of the reviewers that ran: the model each used, what it found, what it cost and how long it took. The review shown took 115 s and 76 credits.

The reviewer table in an IonWarp pull-request comment: three reviewers on DeepSeek V4.1 Flash, the finding checker and the planner, with each one's cost and time — 76 credits and 115 s in all.

IonWarp, Snyk and the rest of a Snyk shortlist

Save 60% vs SnykIonWarp$49/moSnyk$125/moAikido$350/moSemgrep$225/moGitHub Advanced Security$245/mo
Reviews pull requests for securitySecurity Review joins the pull requests that touch auth, input, data access or secretsPass/fail pull request checks; inline comments on up to 10 Snyk Code issues[1][2]PR checks and inline comments from Basic up; not on Free[3][4]PR and MR comments, on every plan[5][6]Dependency review and AI Scan during pull request review[7]
Says how an attacker would use itEach finding names the actor, the path and what they gainNot listedNot listedNot listedNot listed
Finds leaked secretsIn the pull request: keys in code, prompts, client bundles and logs — not git historySnyk Secrets, generally available Aug 2026; the plans page prices it on Enterprise credits[8][9]Secrets detection, on every plan[3]Semgrep Secrets, $15 per contributor; not on Free[5]Secret scanning, and push protection that blocks commits with secrets[7]
Scans a whole branchA full-branch security audit you start from the appTests each imported project: 100 Snyk Code tests a month on Free, 1,000 on Team[9]10 repositories on Free, 100 on Basic[3]Full scans; Free covers up to 10 repositories[5]Code scanning, in Code Security[7]
Known-vulnerable dependenciesNo CVE database: keep GitHub's Dependabot for packagesSnyk Open Source, on every plan[9]Dependency scanning, on every plan[3]Supply Chain, free for up to 10 contributors[5]Dependabot security updates, free on every plan[10]
How a finding gets fixedYour coding agent fixes it from the finding's prompt; IonWarp re-checks the pushOpens a fix pull request for each new actionable vulnerability[11]AutoFix pull requests: 10 a month on Free, unlimited from Basic[3][12]Autofix, on every plan[5]Copilot Autofix suggests fixes for code scanning alerts[7]
Code review in the same appCode Review on each pull request, in one comment with the security findingsNot listedPR code quality checks from Basic up[3]Not listedNot listed
Free planStarter: free for 3 peopleFree: 5 projects, 100 Snyk Code tests a month[9]Free for 2 users and 10 repositories[3]Code and Supply Chain free for up to 10 contributors and 10 repositories[5]Public repositories only: secret scanning, push protection, Copilot Autofix[10]
What 5 developers pay a month$49/mo for 5 developers — one Pro workspace with 5 seats included.$125/mo for 5 developers — Team at $25 each, 5-developer minimum, billed monthly.[13]$350/mo on Basic, a flat fee that includes 10 users (US pricing).[3]$225/mo for 5 developers — Teams, Code + Secrets at $45 each, $30 for Code plus $15 for Secrets.[5]$245/mo for 5 developers — Code Security + Secret Protection at $49 each, per active committer, on a GitHub Team or Enterprise plan.[10]
Git platformsGitHub, and GitHub Enterprise on EnterpriseGitHub, GitLab, Bitbucket and Azure Repos.[14]GitHub, GitLab, Bitbucket and Azure DevOps.[4]GitHub, GitLab, Bitbucket and Azure DevOps.[6]GitHub.[7]

Competitor facts are from each vendor's own pages, dated in the sources below. “Not listed” means the vendor's pages name no such feature; prices are for 5 developers on the team plan each price cell names.

Sources

  1. Pull Request checksSnyk docs · read
  2. Pull Request experienceSnyk docs · read
  3. PricingAikido Security · read
  4. AutoFix Suggestions and Inline Commenting for PR ChecksAikido help · read
  5. Pricing and PlansSemgrep · read
  6. Supported source code managersSemgrep docs · read
  7. About GitHub Advanced SecurityGitHub Docs · read
  8. Snyk Secrets Now Generally AvailableSnyk · read
  9. Snyk Plans and PricingSnyk · read
  10. GitHub Advanced Security plansGitHub · read
  11. Enable automatic Fix PRsSnyk docs · read
  12. Automatic Creation of Pull RequestsAikido help · read
  13. Get started with your Snyk Team planSnyk · read
  14. SCMsSnyk docs · read

Try IonWarp on your next pull request

Install the read-only GitHub App and pick your repositories. Your next pull request gets a review comment.

Starter is free for 3 people · Pro is $49/mo for 5 seats

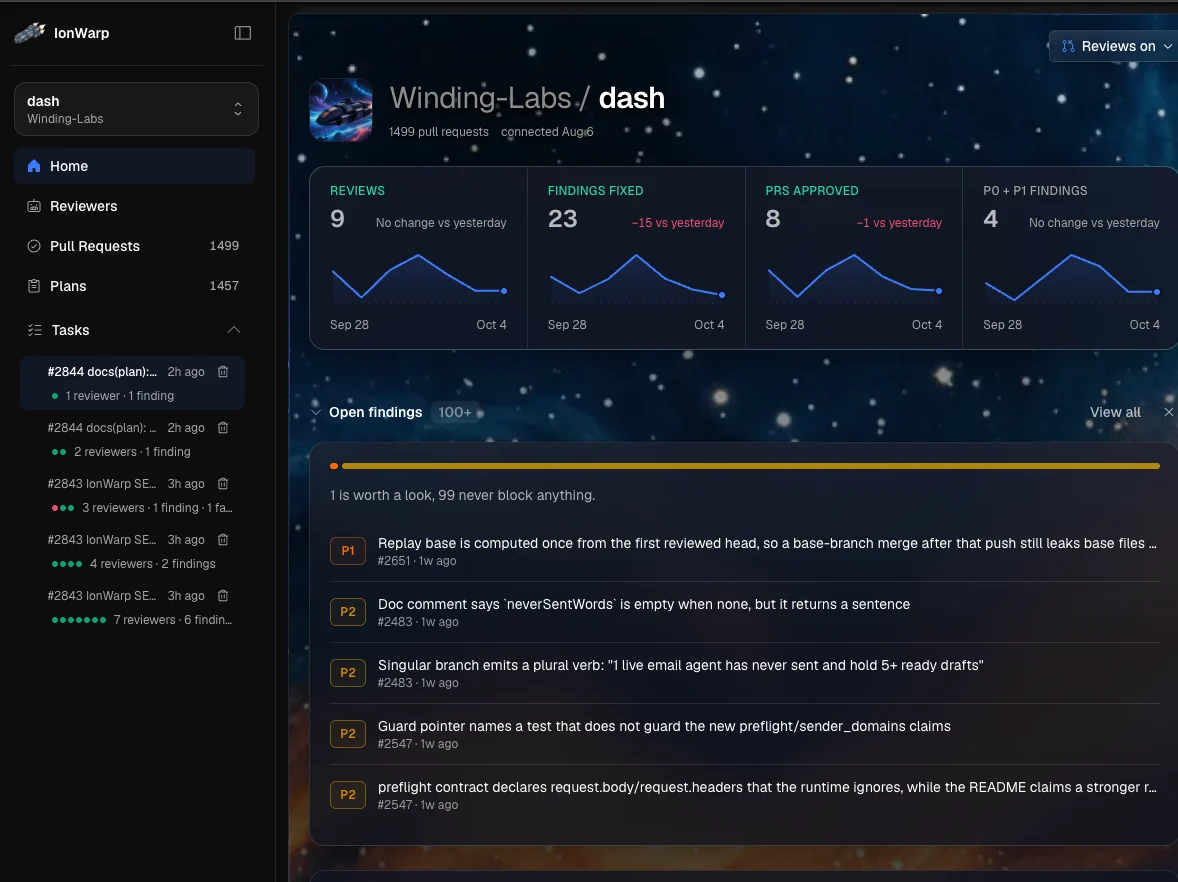
An IonWarp workspace home: reviews, findings fixed, pull requests approved and P0/P1 findings by day, then the open findings by severity.