Security code review
Security code review on every pull request.
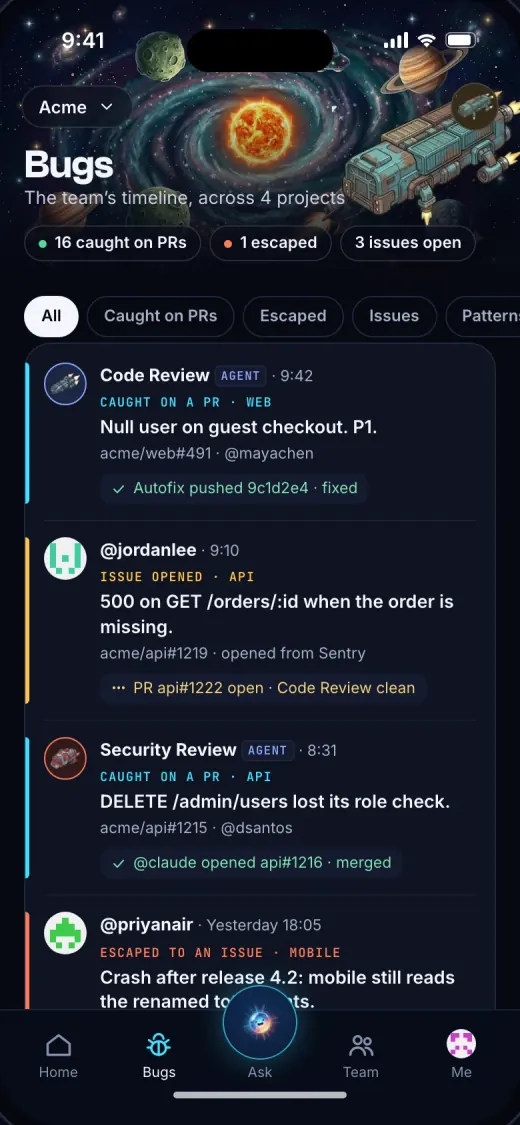
Flags the login route your agent wrote with no role check, on the line, before merge.
9:41
‹PR #1207Finding 1 of 3
 Security ReviewP1
Any signed-in user can delete users
app/api/admin/users.ts
18export async function DELETE(req) {19−await requireRole(req, 'admin');20const { id } = await req.json();
The role check was removed in this PR. The route is reachable from the dashboard, so any member token can call it.
@claudeCopy prompt
Also on this PR
- P1SQL built from a template stringlib/db/search.ts
- P2axios 1.5.1 has CVE-2023-45857package.json
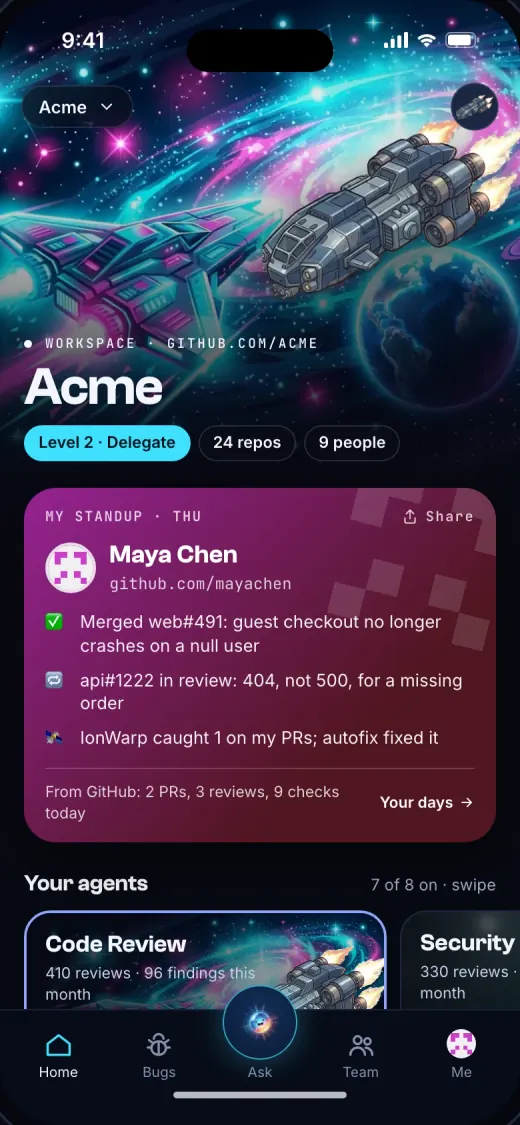
HomeBugsTeamMy Standup
Read-only code accessNever pushes a commit



How it works
Install the GitHub App
Pick the repositories. IonWarp reads the code and comments on pull requests. It never pushes a commit.
Open a pull request
Security Review reads the diff. Finds auth gaps, injection, exposed secrets and vulnerable dependencies.
Fix it with your agent
Every finding has a fix prompt for Claude Code, Cursor or Codex. Push the fix and IonWarp checks it again.
Specialist reviewers
Add AI Architecture
to your pull requests.
IonWarp is a next-gen AI code reviewer for GitHub pull requests, built on open models.
IonWarp AI Architecture vs AI reviewers:8% less wait · 69% cheaperon DeepSeek V4.1 Flash, same 11 PRs →
 IonWarpbotexample review
IonWarp Review — PR #733
| # Sev | Issue | File |
|---|---|---|
| 1 | Second formatPrice() next to the shared one | components/cart/price.ts |
| 2 | v1 handler is still routed | app/api/v1/orders.ts |
| 3 | Feature flag checked in three places | lib/flags/use-flag.ts |
1+export function formatPrice(cents: number) {2+return '$' + (cents / 100).toFixed(2);3+}
lib/money.ts already formats prices with the user’s currency. This copy hard-codes dollars, so EU carts show the wrong symbol.
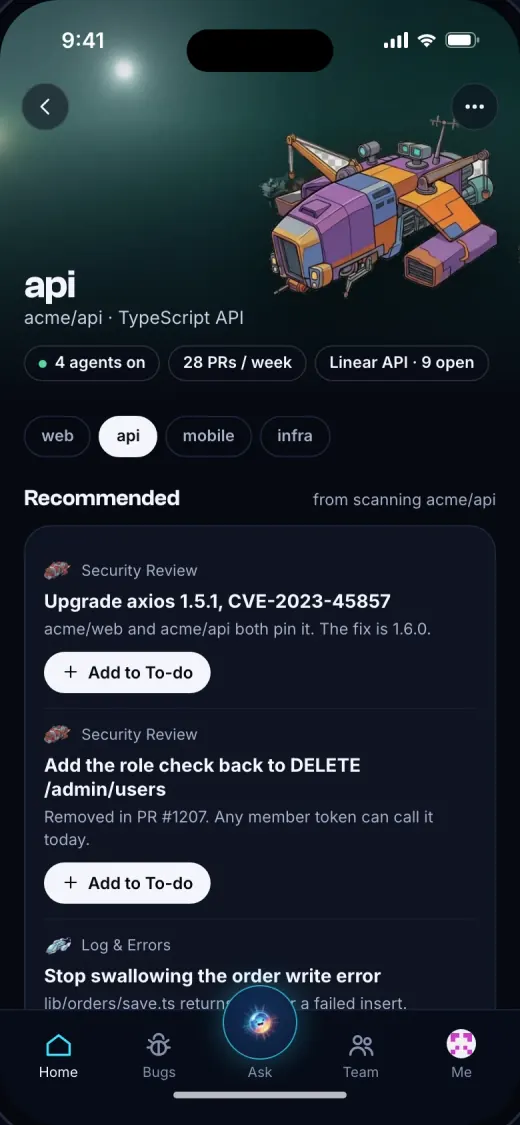
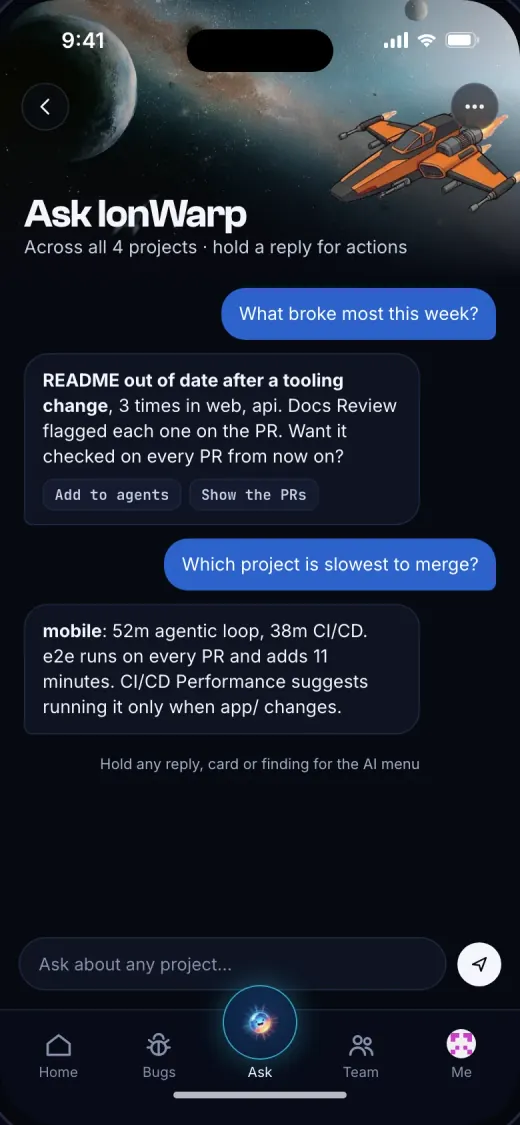
What Security Review catches
Missing permission checks
Routes, server actions and jobs that skip the role check or trust a client id.
Unsafe queries and commands
SQL, shell and HTML built from user input.
Secrets and vulnerable packages
Keys pasted into code, and dependencies with a known CVE.
How each reviewer scores.
On 13 real pull requests with 18 known issues, Security Review runs on DeepSeek V4.1 Flash: F1 62.5%, 5m 56s a review at the median, $0.063 in model cost. Qodo v2 leads on F1 at 73.3%, at ~$1.67 a review. This lane is provisional until its case set grows and its labels are reviewed.
| Model / App | Reviewer Score | F1 | Latency | $/run |
|---|---|---|---|---|
| IonWarp · GLM 5.3 Flash | 88.5 | 66.7% | 1m 38s | $0.012 |
| IonWarp · DeepSeek V4.1 FlashRuns on your PRs | 63.4 | 62.5% | 5m 56s | $0.063 |
| Qodo v2 | 62.8 | 73.3% | 7m 16s | ~$1.67 |
| IonWarp · Muse Spark 1.3 | 42.2 | 44.4% | 2m 30s | $0.258 |
| Greptile v4.1 | 40.2 | 53.8% | 5m 02s | ~$1.75 |
| IonWarp · Grok 4.6 | 39.7 | 53.3% | 7m 42s | $0.575 |
| IonWarp · Gemini 3.8 Flash | 38.5 | 51.6% | 7m 10s | $0.520 |
| CodeRabbit | 34.8 | 54.0% | 9m 26s | ~$1.50 |
| Cursor Bugbot | 31.3 | 50.0% | 8m 23s | ~$1.25 |
| IonWarp · DeepSeek V4 Pro | 31.3 | 34.8% | 2m 40s | $0.131 |
| IonWarp · GPT 5.6 Luna Pro | 31.2 | 28.6% | 1m 16s | $0.105 |
Reviewer Score = (3 × F1 + time + $/run) ÷ 5, each part 0 to 100 within this table. IonWarp rows cost the model’s inference; ~$ is each app’s list price for 5 seats at 100 reviews a month. Provisional scoped-label matching. Release 2026-10-12, CC BY 4.0.
Security Review
IonWarp inferenceApp price estimatesF1 on the same 13 open-source pull requests for every reviewer
IonWarp, Snyk, Semgrep, Aikido and GitHub Advanced Security
Scanners match known patterns and vulnerable packages; a reviewer reads the change. Many teams run both. Every rival cell is cited to the vendor’s own page.
| Feature | IonWarp | Snyk[1] | Semgrep[3] | Aikido[5] | GitHub Advanced Security[6] |
|---|---|---|---|---|---|
| Reviews pull requests for security | Yes: Security Review on every pull request, on the changed lines and the code they call | Yes: Pull request checks and comments | Yes: Pull request comments | Yes: PR Security Review, from Basic | Yes: Code scanning and dependency review on pull requests |
| Finds leaked secrets | Yes: Keys and tokens in the pull request: code, config, logs | Partly: Snyk Secrets, priced on Enterprise credits | Yes: Semgrep Secrets, $15 per contributor | Yes: Secrets detection, every plan | Yes: Secret scanning and push protection |
| Known-vulnerable dependencies | Partly: Flags a package the PR adds when it has a known CVE; no CVE database, so keep Dependabot | Yes: Snyk Open Source, every plan | Yes: Supply Chain, free up to 10 contributors | Yes: Dependency scanning, every plan | Yes: Dependabot, free on every plan |
| How a finding gets fixed | Yes: A fix prompt for your coding agent, or tag @claude on the PR | Yes: Fix and upgrade pull requests | Yes: Autofix | Yes: AutoFix, 10 a month free, unlimited paid | Yes: Copilot Autofix |
| Code review in the same app | Yes: Code Review and six more agents, one comment | No: Not listed | No: Not listed | Yes: PR code quality checks, from Basic | No: Not in these plans |
| Free plan | No: 14-day trial, then Pro | Yes: Free: 5 projects, 100 Code tests a month | Yes: Code and Supply Chain, up to 10 contributors | Yes: 2 users, 10 repositories, no PR review | Partly: Public repositories only |
| 5 developers, a month | $49 a month on Pro, for 5 seats. Code Review and Security on 100 pull requests use about $16 of the $25 of review spend Pro includes. | Team from $25 a month (the page does not say per developer) | $375 a month: Code, Supply Chain and Secrets at $75 per contributor | $300 a month on Basic, which includes 10 users | $265 a month: Code Security $30 + Secret Protection $19 per committer, on GitHub Team ($4) |
Each vendor’s column is read from its own pricing page and docs on 2026-11-12. We also publish a comparison of ten SAST tools by price, Git host and AI at sasttools.com.
Sources
- Snyk, Plans, read 2026-11-12.
- Snyk docs, Pull Request checks, read 2026-11-12.
- Semgrep, Pricing, read 2026-11-12.
- Semgrep docs, GitHub PR comments, read 2026-11-12.
- Aikido, Pricing, read 2026-11-12.
- GitHub, Security plans, read 2026-11-12.
- GitHub, Pricing, read 2026-11-12.
Pricing
Simple pricing for your whole team.
One workspace price with seats included. Every agent on every plan, and a monthly budget IonWarp stays inside. 14 days free, no card.
ProMost popular
One team, every agent from day one.
- 5 seats included
- All eight agents, every repo you connect
- $25 of review spend a month
- A monthly budget you set
Max
Bigger teams and a bigger review budget.
- 10 seats included
- All eight agents, every repo you connect
- $100 of review spend a month
- A monthly budget you set
- Priority models and support
More than 10 people?
Tell us how many seats and how much review spend you need, and we will set up the workspace.
FAQ
Frequently asked questions
Is this SAST?
It does what SAST does on the diff, and it reads the code around it, so it can tell a real missing check from a harmless pattern.
Does it replace Snyk or Dependabot?
It complements them. IonWarp flags the vulnerable package in the PR that adds it and tells you which code path calls it.
Does my code train a model?
No. Reviews run through OpenRouter on providers that do not train on or keep your code. See the security page for the details.
How accurate is Security Review?
On 13 real pull requests with 18 known issues, Security Review runs on DeepSeek V4.1 Flash: F1 62.5%, 5m 56s a review at the median, $0.063 in model cost. Qodo v2 leads on F1 at 73.3%, at ~$1.67 a review. This lane is provisional: its case set is small and still under review, so read it as a direction, not a ranking. Every row, PR and judge verdict is public.
What does it cost?
Pro is $49 a month per workspace with 5 seats and $25 of review spend included. Max is $149 with 10 seats and $100. Every agent is in both. Start with a 14-day trial, no card.
More on security review
More on security review
Ship the fix, not the breach.
Try for free14 days free, no card. Then Pro is $49 a month per workspace with 5 seats, or Max $149 with 10.